


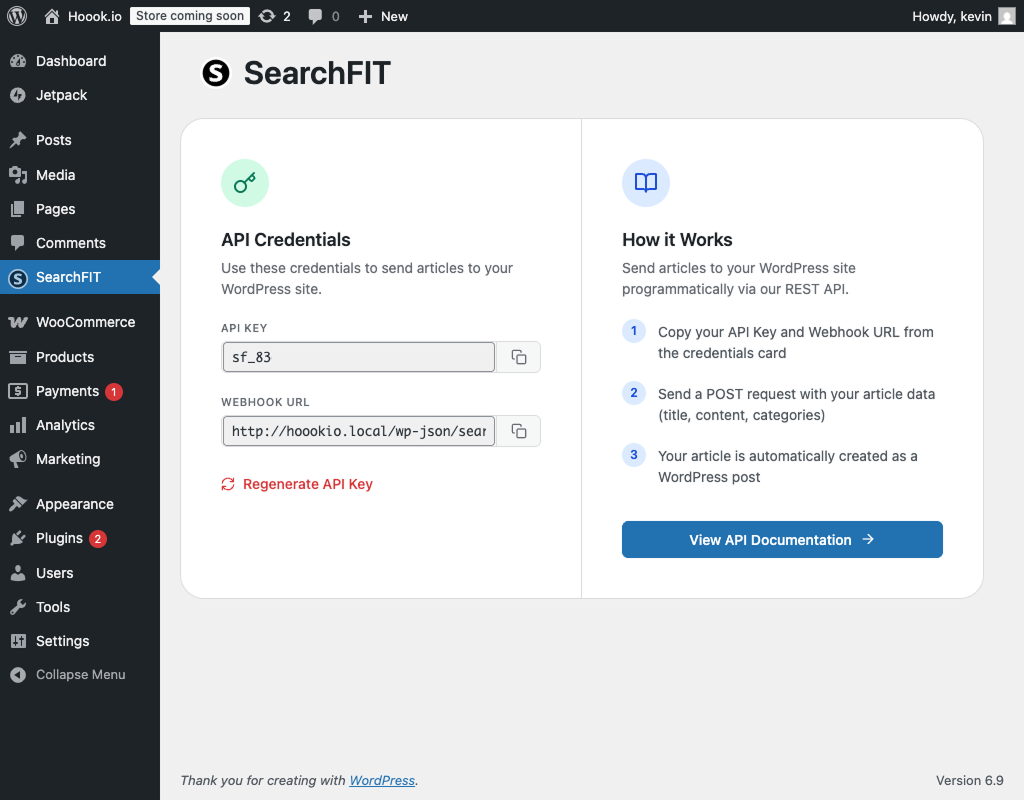
Dashboard with API credentials and copy buttons.
SearchFIT gives you two ways to get content into WordPress. Webhook mode exposes a REST endpoint that lets you create, update, and list posts using an API key — accepting an incoming payload as-is. Import mode lets an administrator bulk-import a SearchFIT content-export CSV straight from the admin screen. Designed for AI content workflows (ChatGPT, Claude, Perplexity), no-code automation (Zapier, Make, n8n), and headless setups.
Features
- Two ingestion modes: accept an incoming webhook payload as-is, or bulk-import a SearchFIT content-export CSV
- Bulk CSV import with Markdown-to-HTML conversion, processed in batches with a live progress bar
- Slug-matched import — re-importing the same CSV updates existing posts instead of duplicating
- Auto-generated cryptographic API key with one-click regeneration
- Create, list, read, and update posts via REST
- Slug-based upsert — re-publishing the same slug updates the existing post instead of duplicating
- Featured images and inline content images downloaded from URLs you supply
- Category and tag management (creates missing categories on the fly)
- Custom post meta with a denylist for WordPress-internal keys
- SEO meta sync to Yoast SEO, Rank Math, SEOPress, and All in One SEO
- Multilingual support via Polylang and WPML
- JSON-LD
<script>blocks extracted, validated, and re-emitted in<head> - Optional embed allowlist for YouTube / Vimeo / SoundCloud / Spotify / Loom / TikTok / Apple Podcasts / Dailymotion
- Settings UI for default post status, author, category, tags, embeds, hero deduplication
- Health check endpoint and activity log
Security
- Cryptographic API key (
random_bytes) with timing-safe comparison - SSRF guard — outbound URL fetches reject private, loopback, link-local, and reserved IPs (IPv4 and IPv6)
- Custom-meta denylist blocks attempts to write
_edit_lock,_thumbnail_id,_wp_*and other WP internals - Iframes are off by default; when enabled, restricted to a strict host allowlist and src forced to https
- JSON-LD payloads are JSON-validated and re-encoded with
JSON_HEX_TAGflags before storage - Settings save flows through the WordPress Settings API (CSRF nonce + sanitize callbacks)
- WAF-friendly: auth runs inside handlers (so failed requests don’t trigger Wordfence/Sucuri lockout heuristics); POST-only methods (no PUT/PATCH); public health endpoint
API Reference
Full docs at searchfit.ai/docs. Quick example:
curl -X POST "https://yoursite.com/wp-json/searchfit/v1/articles" \
  -H "Content-Type: application/json" \
  -H "X-API-Key: YOUR_API_KEY" \
  -d '{
    "title": "My AI-Generated Article",
    "slug": "my-ai-article",
    "content": "<p>Your content here...</p>",
    "status": "draft",
    "categories": ["AI", "Technology"],
    "tags": ["ai-content", "automation"],
    "meta_description": "Short SEO description.",
    "featured_image_url": "https://example.com/image.jpg"
  }'
Privacy Policy
SearchFIT does not collect or transmit any personal data. API keys and the webhook activity log are stored in the WordPress database and never sent to external servers.