
Sarala Login Page – Social Login & Login Security
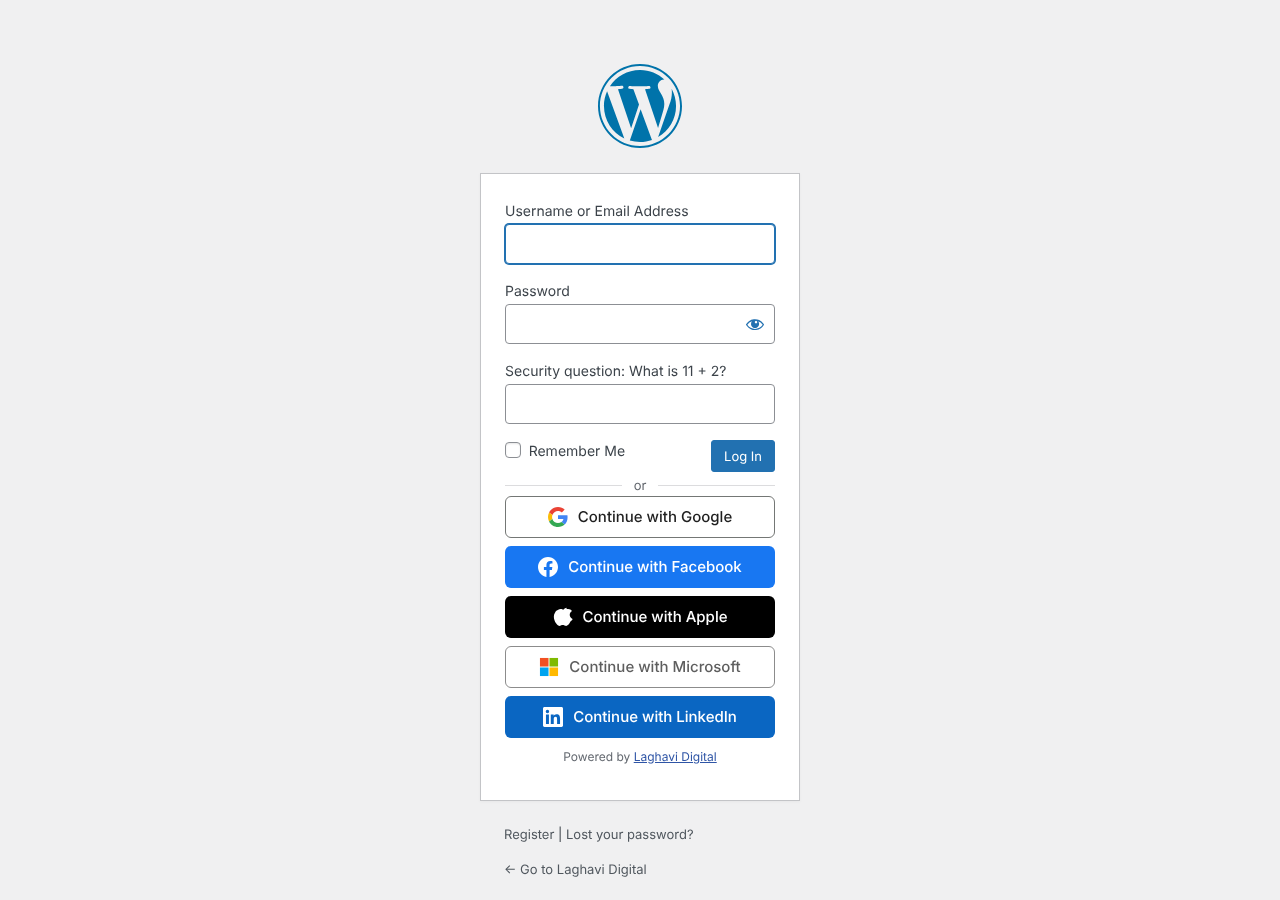
Social login buttons on the WordPress login page, with the math security question.
Sarala Login Page adds one-click social login and sign-up to WordPress and WooCommerce, and protects your login page at the same time. Visitors log in with the accounts they already have, you stop bots and brute-force attacks, and everything is set up from one simple screen. No account with us, no tracking, no locked features.
Features at a glance
- Social login and registration: Google, Facebook, Apple, Microsoft, LinkedIn, X (Twitter), GitHub, Discord, Reddit and Yahoo.
- Forgery-proof logins: ID token signatures are checked against each provider’s live public keys, so nobody can fake a social login to get into your site.
- WooCommerce login: My Account, registration and checkout (guests sign up and come back to checkout with their cart).
- Limit login attempts: lock out IP addresses after too many failed logins.
- Custom login URL: hide wp-login.php and wp-admin from bots.
- Force password reset: make passwords expire after a number of days.
- Login CAPTCHA: a simple math question on login and registration forms, no Google reCAPTCHA needed.
- Failed login log: every failed attempt with IP address, device and location.
- Connected accounts: users connect and disconnect social accounts from their profile.
- Shortcode
[sarala_login_page]to place the login buttons on any page, with any theme or page builder.
Social login providers
Visitors create an account or log in with one click using the accounts they already have:
- Apple (Sign in with Apple)
- Microsoft (personal, work and school accounts)
- X (Twitter)
- GitHub
- Discord
- Yahoo
- Reddit (Reddit never shares email addresses, so people connect Reddit to an existing account from their profile and then log in with it)
Works with WordPress and WooCommerce
- Buttons on the WordPress login and registration pages.
- Buttons on the WooCommerce My Account login and registration forms.
- Buttons at the top of the WooCommerce checkout, so guests can sign up or log in and come straight back to checkout with their cart kept.
- WooCommerce’s own “create an account during checkout” option keeps working.
- A
[sarala_login_page]shortcode to place the buttons anywhere.
The right role for every new account
- If WooCommerce is active, every new sign-up becomes a Customer.
- If not, new sign-ups get the “New User Default Role” from Settings > General (Subscriber by default).
- Admins can change any user’s role at any time from Users, as usual.
Existing users log straight in
If someone already has an account with the same email address, logging in with Google, Facebook or another provider takes them straight into that account and connects it automatically. For safety this only happens when the provider has verified the email address. Users can also connect and disconnect accounts from their profile (or from My Account > Account details with WooCommerce), and admins see which accounts each user has connected in a “Social login” column on the Users screen.
Bot protection with a simple math question
The login and registration forms (WordPress and WooCommerce) ask one random question, for example “What is 7 + 9?”. The answer is checked on the server, so bots that skip the form cannot get past it. The REST API, XML-RPC and application passwords are not affected.
Limit login attempts
After 5 failed logins within 15 minutes (you choose the numbers), the IP address is locked out for 30 minutes, even if it then tries the right password. This works on wp-login.php, WooCommerce, XML-RPC and the REST API. You can add your own IP addresses to a “never lock out” list, and see and unlock locked-out addresses on the Failed logins screen.
Force password reset
Make passwords expire after a number of days you choose (for example 90), for every role or only the ones you pick. When a password is too old, the login is refused and the user is emailed a link to choose a new one. Existing users start counting from their next login, so nobody is locked out the moment you switch it on.
Built to be safe
- Standard OAuth 2.0 / OpenID Connect with a one-time state value tied to the visitor’s browser.
- Secrets are never shown again after saving.
- No tracking and no data sent anywhere except to the login provider the visitor chooses.
Made by Laghavi Digital (Laghavi FZE LLC). Plugin page: laghavi.site/sarala-login-page.
External services
This plugin connects to the login provider a visitor picks, only when they click its button. The site owner must create an app with each provider they enable and agree to that provider’s terms.
When a visitor clicks a button, their browser is sent to the provider’s login page. After they agree, the provider sends back a one-time code, and the site exchanges it (server to server) for the visitor’s basic profile: their account ID, name and email address. Nothing else is sent or requested.
- Google – accounts.google.com, oauth2.googleapis.com, openidconnect.googleapis.com. Terms, Privacy
- Facebook (Meta) – www.facebook.com, graph.facebook.com. Terms, Privacy
- Apple – appleid.apple.com. Terms, Privacy
- Microsoft – login.microsoftonline.com, graph.microsoft.com. Terms, Privacy
- LinkedIn – www.linkedin.com, api.linkedin.com. Terms, Privacy
- X (Twitter) – x.com, api.x.com. Terms, Privacy
- GitHub – github.com, api.github.com. Terms, Privacy
- Discord – discord.com. Terms, Privacy
- Reddit – www.reddit.com, oauth.reddit.com. Terms, Privacy
- Yahoo – api.login.yahoo.com. Terms, Privacy
To check that a login really comes from the provider, the plugin also downloads the provider’s public signing keys (Google: www.googleapis.com/oauth2/v3/certs, Apple: appleid.apple.com/auth/keys, Microsoft: login.microsoftonline.com, LinkedIn: www.linkedin.com/oauth/openid/jwks, Yahoo: api.login.yahoo.com/openid/v1/certs). Nothing is sent in these requests; the keys are kept for a few hours.
The plugin stores the visitor’s provider account ID and email on their WordPress user so they can log in again. This data is deleted when the plugin is deleted.
IPinfo (ipinfo.io) – optional, off by default. Only when you tick “Look up city and country for each IP” in Sarala Login Page > Settings, the plugin sends the IP address of each failed login attempt (and your IPinfo token, if you entered one) to ipinfo.io, when an administrator opens the Failed logins screen, to show the approximate city, region and country. Each result is kept for a week, so an address is looked up at most once a week. Terms, Privacy