
JM Website Security Hardening
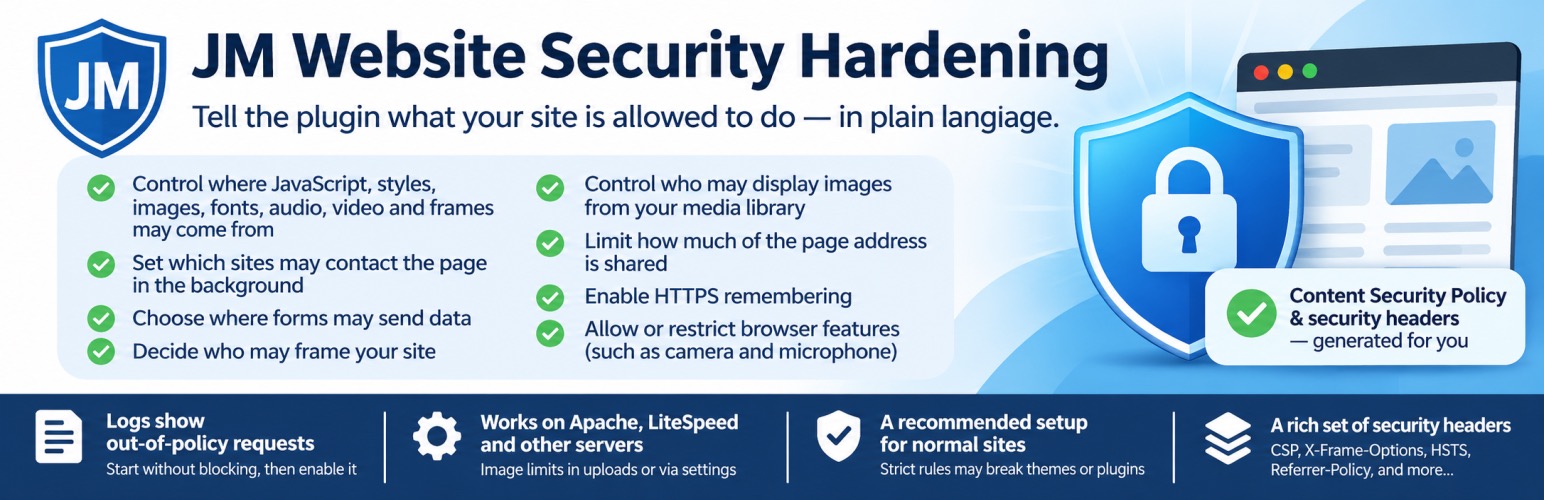
JM Website Security Hardening asks what the site is allowed to do, in plain language, and sends the matching browser rules.
You choose:
- where JavaScript, styles, images, fonts, audio, video, and frames may come from
- which sites the page may contact in the background
- where forms may send their data
- who may place this site inside a frame
- who may display images hosted in the media library
- how much of the page address is shared with the next site
- whether the browser should remember HTTPS
- which browser features, such as the camera and the microphone, a page may use
The plugin writes the Content Security Policy and the related security headers from those answers. A log shows addresses that fell outside the rules, so you can start without blocking anything and turn blocking on when the result looks right.
The recommended answers suit a normal site. Strict answers refuse code written directly in the page and can break a theme, a plugin, the dashboard, or the login screen.
Image hotlinking uses root .htaccess on Apache and LiteSpeed: rewrite lines also go through mod_rewrite_rules, and the full BEGIN JMWSH / END JMWSH block (including Cross-Origin-Resource-Policy in “only this website” mode) is written with insert_with_markers(). On nginx the settings screen shows the matching server-block configuration to paste.
Headers
Depending on the answers, the plugin can send:
- Content-Security-Policy, or Content-Security-Policy-Report-Only
- X-Frame-Options
- X-Content-Type-Options
- X-XSS-Protection
- X-Permitted-Cross-Domain-Policies
- Referrer-Policy
- Permissions-Policy
- Strict-Transport-Security, only on HTTPS
- Cross-Origin-Opener-Policy
- Report-To and Reporting-Endpoints
- Cross-Origin-Resource-Policy, on image files when only this site may display them
Developer hooks
jmwsh_settingsfilters the normalized settings before headers are built.jmwsh_headersfilters the final header names and values.jmwsh_download_hostsfilters the host names allowed to display hosted files.jmwsh_mod_rewrite_rulesfilters the hotlink rewrite lines added throughmod_rewrite_rules.jmwsh_htaccess_rulesfilters the Apache lines written withinsert_with_markers()into the root.htaccessblock for static files.