
Beplus Security Headers & Script Auditor
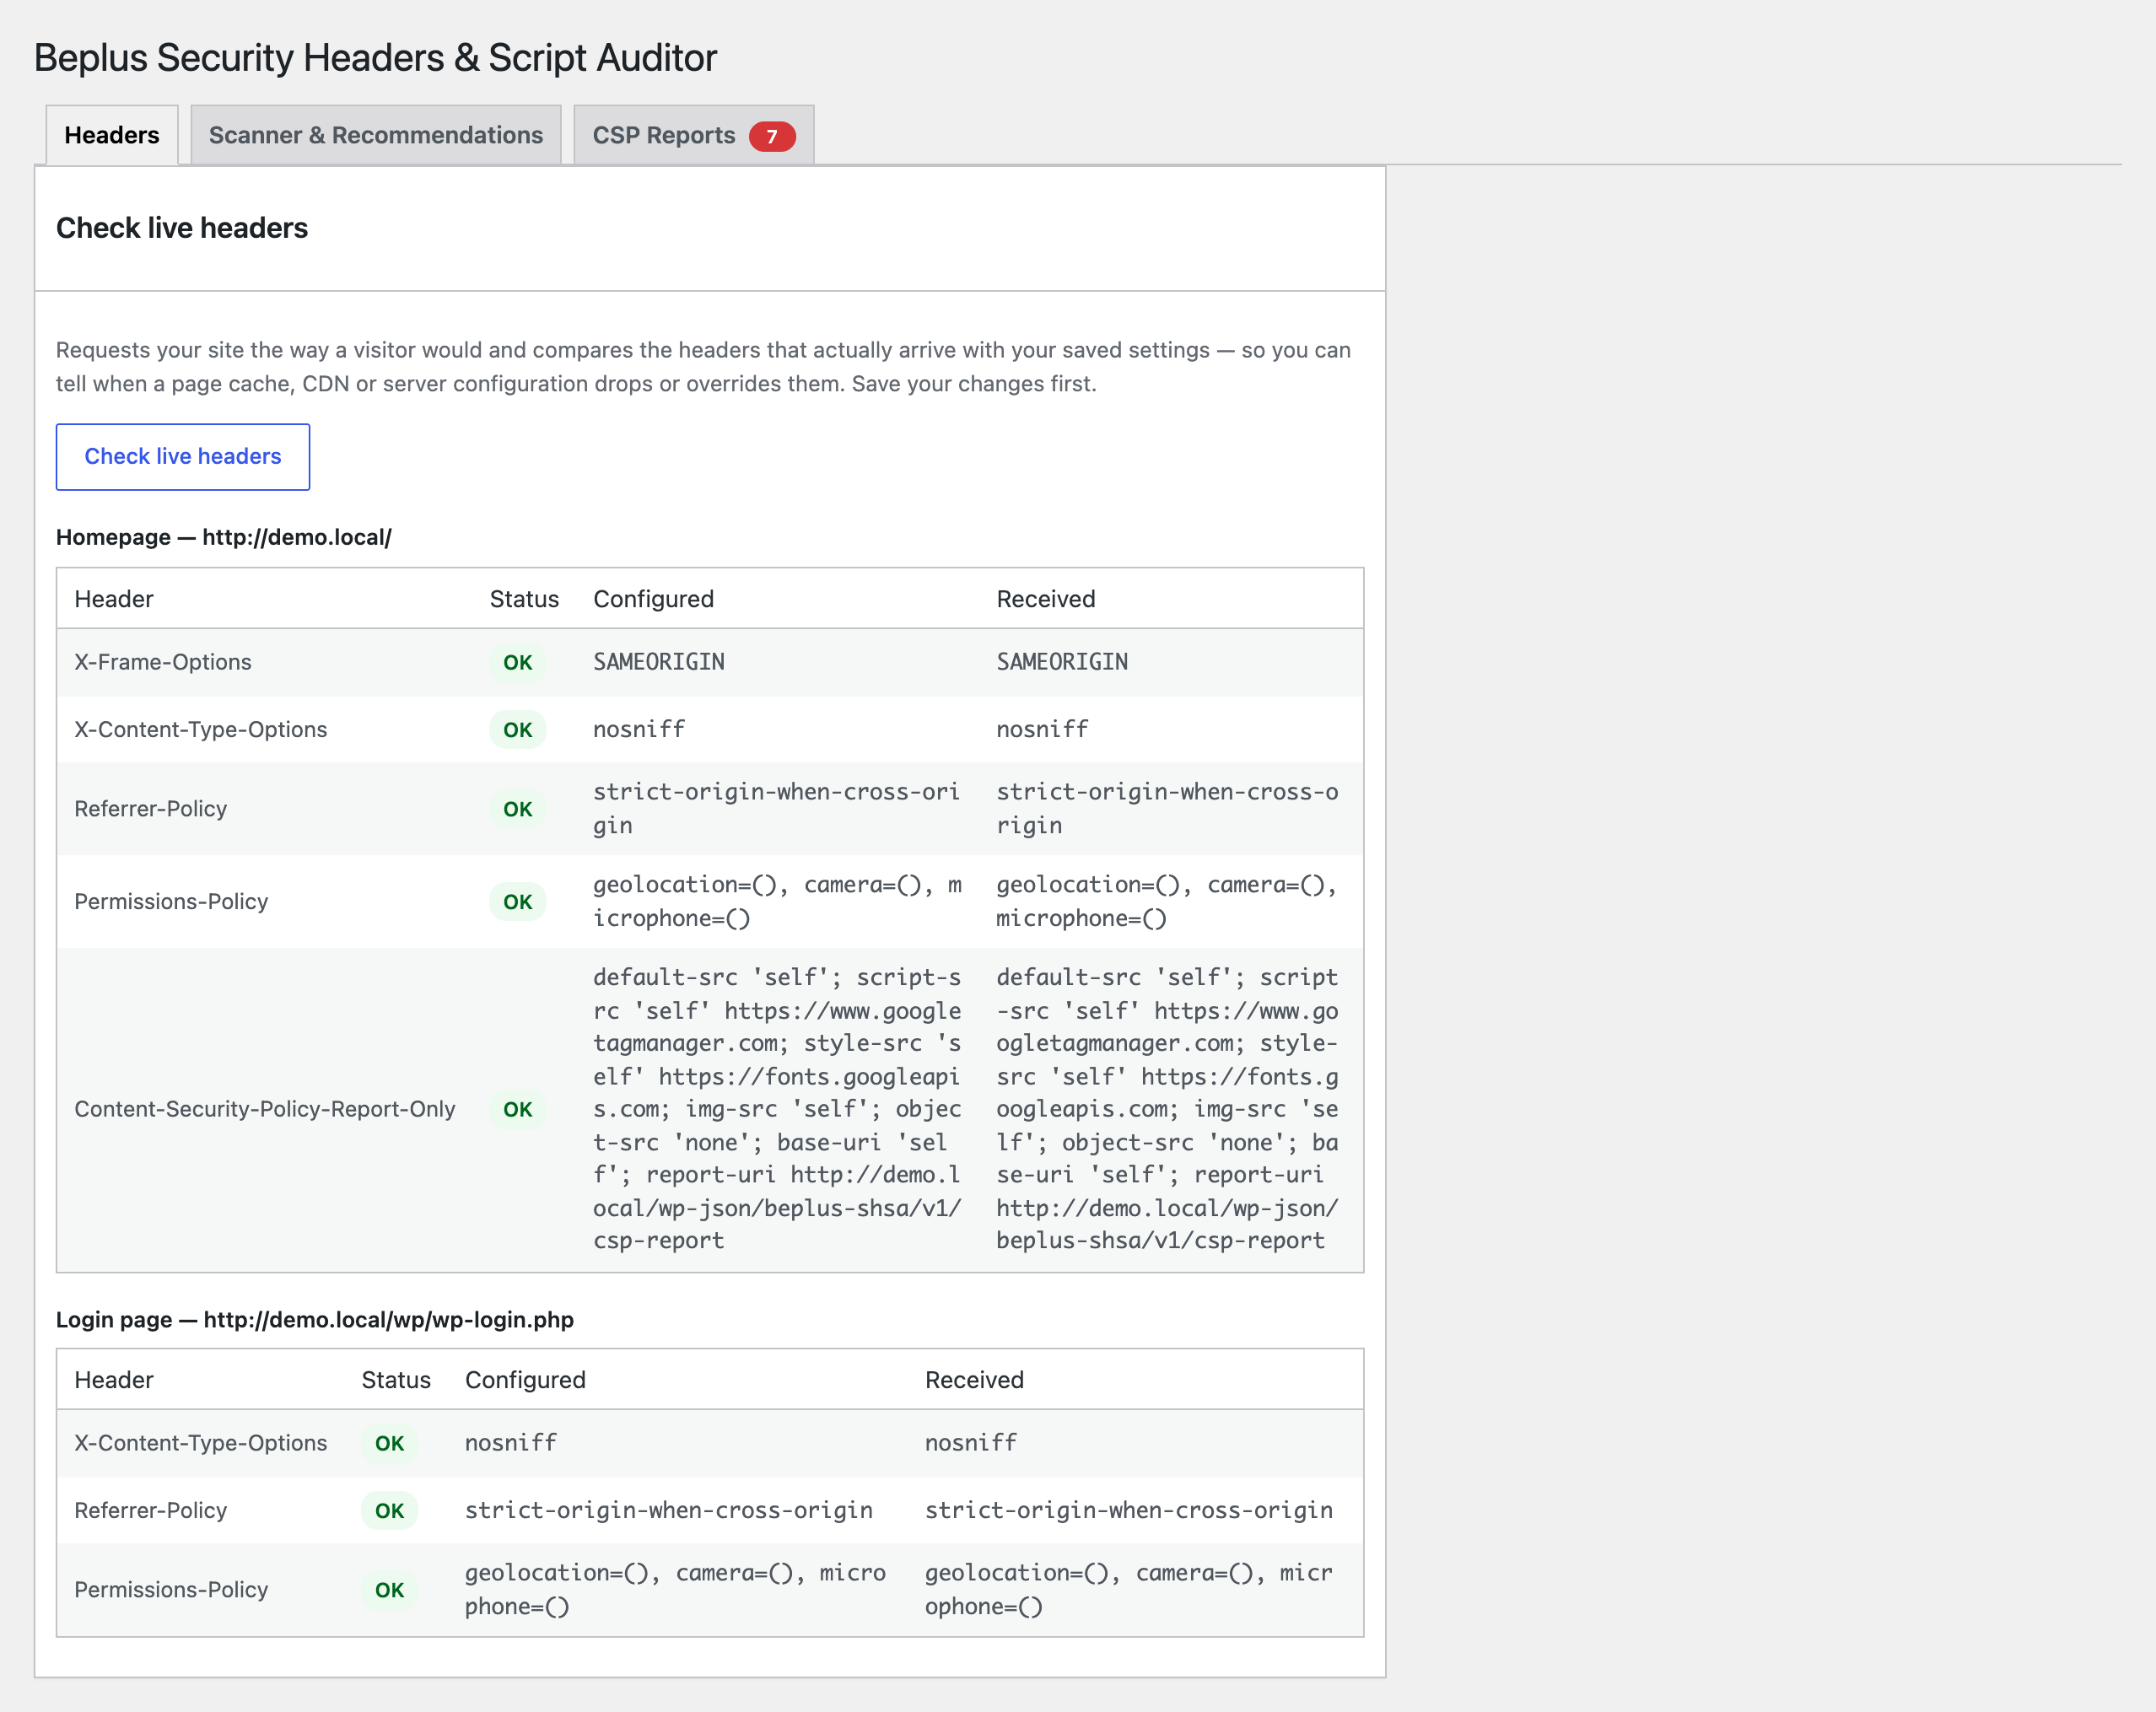
The Headers tab with the live header check, showing which headers actually reach visitors.
Beplus Security Headers & Script Auditor gives WordPress site owners everything needed to add security headers — and a Content-Security-Policy — without breaking their site:
- Security header toggles — enable X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Strict-Transport-Security, Permissions-Policy, Content-Security-Policy (with an optional report-only mode), and the legacy X-XSS-Protection header, each with sensible defaults. Headers are sent on your public pages and, optionally, on wp-admin, the login page and the REST API too.
- A live header check — requests your site the way a visitor would and shows which headers actually arrive. If a page cache, CDN or server configuration drops or overrides a header, you’ll see it.
- A scanner — fetches your homepage, or optionally your whole site (up to 200 of your most recently published posts/pages), and lists every external script, stylesheet, font, image, video/audio, iframe and form target it finds, plus inline scripts/styles. Well-known services such as Google Fonts, Google Analytics, Stripe and reCAPTCHA also get the extra origins they load at runtime, so the suggested policy doesn’t break them.
- Recommendations you control — every finding is listed as a checkbox row; uncheck anything you don’t want, and the Content-Security-Policy preview updates live. Apply the checked rows to the CSP field with one click, review it, then press Save. Nothing is ever applied automatically.
- CSP violation reports — in report-only mode, visitors’ browsers report what the policy would block to your own site. The CSP Reports tab lists each blocked resource with a one-click “Add to policy” button, so you can tighten your policy from real data before enforcing it.
There’s also a repeatable table for adding any other custom response header your site needs.
Why use this plugin
- No external service calls, tracking, or phone-home behaviour — the scanner and header check only request pages on your own site, and CSP reports are sent by browsers to your own site.
- Every setting is sanitized on save, and header values are stripped of line breaks to prevent HTTP header injection.
- Sensible, conservative defaults: only X-Frame-Options, X-Content-Type-Options, and Referrer-Policy are enabled out of the box. HSTS, Permissions-Policy, CSP, and X-XSS-Protection are opt-in since they can affect how your site behaves and should be reviewed first.
Privacy
When “Collect violation reports” is turned on, visitors’ browsers send Content-Security-Policy violation reports to a REST API endpoint on your own site (/wp-json/beplus-shsa/v1/csp-report). The plugin stores only the violated directive, the blocked origin or keyword (e.g. https://cdn.example.com or inline), the path of the page, a count and timestamps. IP addresses, user agents, query strings and full URLs are never stored. Reports are kept until you clear them or uninstall the plugin. This feature is off by default.