
Atlant Security

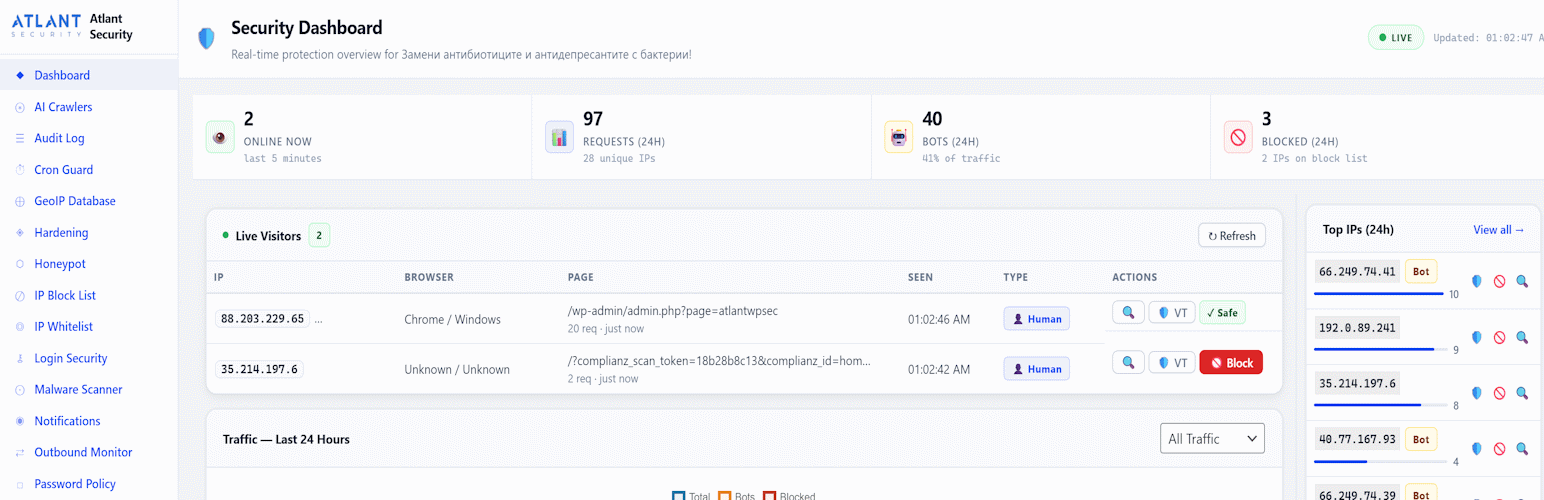
Security Dashboard: the protection status strip, visitors online now, requests, bots and blocks, live visitors, traffic and top IPs.
Atlant Security protects a WordPress site from the first byte of a request to the clean-up after a break-in: a firewall with rate limits, brute-force and two-factor login protection, a file and database malware scanner, hardening that is verified on your own server, alerts, a visitor log and an audit log, and a post-breach recovery toolkit. Everything runs on your server, with no external dependencies.
Every setting is one search away. Type in the box at the top of the plugin menu, or press “/”, and it finds any setting on any of the plugin’s pages and takes you straight to it.
Layered Defense
- Early-request firewall – the WAF, rate limiter and IP block list inspect every request at
initpriority 0, before the page is built and before other plugins handle it. - Logins and accounts – lockouts, CAPTCHA, a custom login URL, 2FA, session security, password and REST API policies.
- Content and configuration – hardening, security headers, AI crawler control and honeypots.
- Outbound and data – SSRF prevention and malware scanning of files and the database.
- Response and recovery – alerts, logs and the Post-Breach Command Center.
Features
Security Dashboard
A protection status strip shows at a glance the firewall mode (with a one-click “Switch to Block” while it only logs), login lockouts, two-factor coverage, rate limits, logging, the security headers grade, the last malware scan, whether PHP can run in uploads, and GeoIP, each linking to its page. Below it: visitors online now (refreshed every 15 seconds), requests, bots and blocks in the last 24 hours, a traffic chart, top IPs and top pages.
Web Application Firewall (WAF)
39 rules in 8 categories: SQL injection, XSS, path traversal and file inclusion, remote code execution, PHP object injection, SSRF, WordPress-specific probes (.env, .git, backups, debug logs, readme files) and scanner fingerprints. Request values are decoded twice more after PHP’s own URL decoding, and HTML entities and \u and \x escapes are resolved, before matching, so encoded payloads are caught. Log Only, Block or Tarpit mode; high-severity matches can block the attacking IP for as long as you choose.
Rate Limits
Sliding-window limits per visitor IP for 10 kinds of request: front-end pages, logins, search, feeds, sitemaps, the REST API (signed-in and anonymous), WooCommerce checkout, XML-RPC and WP-Cron. The WAF page shows every limit, lets you change it, and counts the requests throttled in the last 24 hours. Uses APCu when available.
Brute Force Protection
Progressive lockouts (5 minutes, then 30 minutes, then 24 hours) after a number of failures you set, with generic login errors that do not reveal whether a username exists. Unlock one IP, or clear every lockout, in one click; every page that can lock you out explains how to get back in. Author ID scans are blocked, and author archive URLs can be rebuilt from display names so they no longer publish login names.
CAPTCHA and Custom Login URL
Cloudflare Turnstile or Google reCAPTCHA v2 or v3 on the login, registration and lost-password forms, off until you choose a provider. Move wp-login.php to a secret address; the plugin asks you to whitelist your own IP first.
Two-Factor Authentication (2FA)
Authenticator apps (Google Authenticator, Microsoft Authenticator, Authy, 1Password and any TOTP app) set up by QR code or key, or codes by email, with 10 recovery codes; require it per role. A password alone never gets in: the session a password-only login creates is revoked on the server before the code is asked for. Anyone who has set up 2FA is asked for a code on every login, each account allows 10 wrong codes in 15 minutes, and API logins for 2FA accounts need an application password.
Malware Scanner
Scans PHP files in WordPress core, plugins, themes, uploads and mu-plugins, checks wp_options and post content for injected scripts, and flags newly created administrator accounts. Core files are verified against the official WordPress.org checksums. 17 signatures cover eval, base64, gzinflate and ROT13 backdoors, web shells (WSO, b374k, China Chopper), crypto miners, card skimmers, malicious redirects, hidden iframes and PHP files in uploads. The scan runs in batches in the background, picks up again after a page reload, can be cancelled, and can run daily on a schedule. Quarantine with one-click restore, a false-positive list with Undo, and CSV export of every finding.
Hardening, Verified on Your Server
One-click hardening (disable XML-RPC and the file editor, hide the WordPress version, block REST API user listing and author scans, force SSL for wp-admin, automatic updates, block PHP execution in uploads) with Enable and Disable buttons, and “How to fix” instructions for what the plugin cannot change itself. Checks report what is actually true: “Block PHP in Uploads” writes the rule into the uploads .htaccess, then requests a test file to confirm the server obeys it, and gives nginx and IIS sites the snippet to paste. A Vulnerability Audit lists everything still open.
Security Headers
HSTS, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, Content-Security-Policy (report-only or enforced), Cross-Origin-Resource-Policy and Cross-Origin-Opener-Policy, with every CSP directive and Permissions-Policy feature configurable and a preview of the exact header that will be sent, plus a letter grade. Removes X-Powered-By.
Session Security
HttpOnly, Secure and SameSite cookies; each session bound to the browser that created it (by User-Agent, and optionally by IP); a limit on concurrent sessions; an optional idle timeout; and a “Who is logged in” list with “Log out everywhere” for each account.
Honeypots and AI Crawlers
Hidden-link traps, a fake login page, and comment and Contact Form 7 fields that only bots fill in. Search engines and the AI crawlers you allow are never banned. Allow or block 20 known AI and LLM crawlers (GPTBot, ClaudeBot, Google-Extended, Bytespider and others) one by one, through robots.txt and with a 403 at the request level.
Outbound Monitor (SSRF Prevention)
Logs every outgoing HTTP request with the plugin or theme that made it, blocks requests to private and internal addresses including cloud metadata endpoints, and can enforce a domain allowlist.
Cron Guard
Takes a snapshot of the scheduled tasks and flags new or unusually frequent ones, a common way for malware to reinstall itself, while recognising every task WordPress core schedules. Detects wp-cron.php floods and helps you move to a real system cron.
Alerts
Email, Slack and custom JSON webhooks, off until you enable them, filtered by a minimum severity. Alerts cover malware, PHP files uploaded through the media library, new administrators, two-factor lockouts, unexpected scheduled tasks, blocked outbound requests, failed two-factor emails, login lockouts, firewall auto-blocks and honeypot bans. Each kind is sent at most once per 15 minutes (lockouts, blocks and bans once per 6 hours) with a count of what was held back, so an attack produces a summary, not a flood. “Send test” shows the mail server’s or webhook’s own answer, a Recent alerts table records what was sent where, and an optional daily digest sums up the day.
Visitor Log and Audit Log
Every request with its IP, country (with the free MaxMind GeoLite2 database), method, page, browser and status, kept for 30 days by default and searchable over the whole period: date ranges, country, method and HTTP status filters, sortable columns, and a CSV export that follows the filters. The audit log records administrator actions (users and roles, plugins and themes, blocks, unlocks and whitelisting, exports) and can be searched, filtered by action, user and date, and exported.
Post-Breach Command Center
The recommended order of response in one place: audit administrator accounts, terminate all sessions, rotate the secret keys and salts, lock the site down, scan the database, reinstall WordPress core and plugins, force a password reset for every user, deactivate plugins, clear caches, and download an incident report. Results stay on screen after the logout these actions cause.
Why Atlant Security?
- Status you can trust – a check passes only when the plugin has verified it on your server, not because a checkbox is ticked.
- One plugin, not five – firewall, logins, scanning, hardening, alerts, logs and recovery share one block list and one whitelist.
- No external dependencies – no CDN, external fonts or telemetry; outside services only for the features you switch on (see External Services).
- Safe Mode – one line in wp-config.php pauses every blocking feature if you lock yourself out.
- Your data, your choice – nothing is deleted on deactivation; deleting the plugin asks whether to keep its data.
- Accessible and multisite-ready – labelled controls, keyboard focus rings and phone layouts; activation and uninstall cover every subsite.
External Services
The plugin contacts these services only when you switch on the feature that needs them.
Cloudflare IP ranges
Used to check that a request really comes from a Cloudflare edge server before the visitor IP in its CF-Connecting-IP header is trusted.
- Data sent: none; the plugin downloads Cloudflare’s public IP range lists.
- When: weekly (cron
aswp_refresh_cloudflare_ips), only while Cloudflare integration is on. - Endpoints: https://www.cloudflare.com/ips-v4 and https://www.cloudflare.com/ips-v6
- Cloudflare Terms of Use, Cloudflare Privacy Policy
MaxMind GeoLite2 database
Downloads the GeoLite2-Country database, which is stored on your server and used to show visitor countries.
- Data sent: your MaxMind license key, to authenticate the download. No visitor data.
- When: when you download it, then weekly (cron
aswp_update_geoip_db), only while GeoIP is on and a license key is set. - Endpoint: https://download.maxmind.com/app/geoip_download
- MaxMind GeoLite2 EULA, MaxMind Privacy Policy
Google IP ranges
Lets requests from Google’s published IP ranges through the plugin’s protections when they also identify as Googlebot or another Google crawler.
- Data sent: none; the plugin downloads a public JSON list of Google IP ranges.
- When: weekly (cron
aswp_refresh_google_ips), only while Google integration is on. - Endpoint: https://www.gstatic.com/ipranges/goog.json
- Google Terms of Service, Google Privacy Policy
Microsoft Bing IP ranges
Lets requests from Bingbot’s published IP ranges through when they also identify as Bingbot.
- Data sent: none; the plugin downloads a public JSON list of Bingbot IP ranges.
- When: weekly (cron
aswp_refresh_microsoft_ips), only while Microsoft integration is on. - Endpoint: https://www.bing.com/toolbox/bingbot.json
- Microsoft Services Agreement, Microsoft Privacy Statement
WordPress.org core checksums
The malware scanner compares WordPress core files with the official checksums; matching files are skipped and changed ones are reported.
- Data sent: your WordPress version and locale. No site or visitor data.
- When: during a malware scan with “Use core checksums” on (the default), at most once a day per WordPress version.
- Endpoint: https://api.wordpress.org/core/checksums/1.0/
- WordPress.org Terms, WordPress.org Privacy Policy
WordPress.org secret keys
Generates new secret keys and salts for the “Rotate Secret Keys” action on the Post-Breach page.
- Data sent: none; the plugin downloads newly generated keys.
- When: only when an administrator clicks Rotate Secret Keys.
- Endpoint: https://api.wordpress.org/secret-key/1.1/salt/
- WordPress.org Terms, WordPress.org Privacy Policy
Slack
Posts alerts to the Slack channel of the incoming webhook you enter.
- Data sent: the alert subject, description and severity, your site URL, and the IP address involved. No cookies or other visitor data.
- When: for each alert at or above your minimum severity, and once a day if the daily digest is on, while Slack alerts are on; and whenever you click “Send test”.
- Endpoint: the Slack incoming webhook URL you enter (https://hooks.slack.com/services/…).
- Slack Terms of Service, Slack Privacy Policy
Custom webhooks
Sends alerts as JSON to the URL you enter, for any monitoring or alerting system.
- Data sent: the alert subject, description and severity, your site URL, a timestamp, and the IP address involved. No cookies or other visitor data.
- When: as for Slack: alerts and the daily digest while webhook alerts are on, and whenever you click “Send test”.
- Endpoint: the URL you enter; its terms and privacy policy are those of the service you choose.
Google reCAPTCHA
Off by default. When you choose reCAPTCHA v2 or v3 as the CAPTCHA provider, it protects the login, registration and lost-password forms you select.
- Data sent by the visitor’s browser: Google’s reCAPTCHA script is loaded from https://www.google.com/recaptcha/api.js, and Google receives the visitor’s IP address and its usual reCAPTCHA signals.
- Data sent by your server: the visitor’s response token, your secret key and the visitor’s IP address, to https://www.google.com/recaptcha/api/siteverify.
- When: only on those forms, only while reCAPTCHA is the chosen provider.
- Google Terms of Service, Google Privacy Policy
Cloudflare Turnstile
Off by default. When you choose Cloudflare Turnstile as the CAPTCHA provider, it protects the login, registration and lost-password forms you select. Cloudflare states that Turnstile does not track users across sites.
- Data sent by the visitor’s browser: the Turnstile script is loaded from https://challenges.cloudflare.com/turnstile/v0/api.js, and Cloudflare receives the visitor’s IP address and its usual Turnstile signals.
- Data sent by your server: the visitor’s response token, your secret key and the visitor’s IP address, to https://challenges.cloudflare.com/turnstile/v0/siteverify.
- When: only on those forms, only while Turnstile is the chosen provider.
- Cloudflare Terms of Service, Cloudflare Privacy Policy